
When Ecobank Uganda's Juliet Kyomugisha, Nation Media Group's Russell Akuom and AAR Hospital's Ibrahim Juma took to the stage at the CITO East Africa Data and Cybersecurity Summit to report back from the roundtable sessions, the consistent message was that implementation is the hard part of data governance.
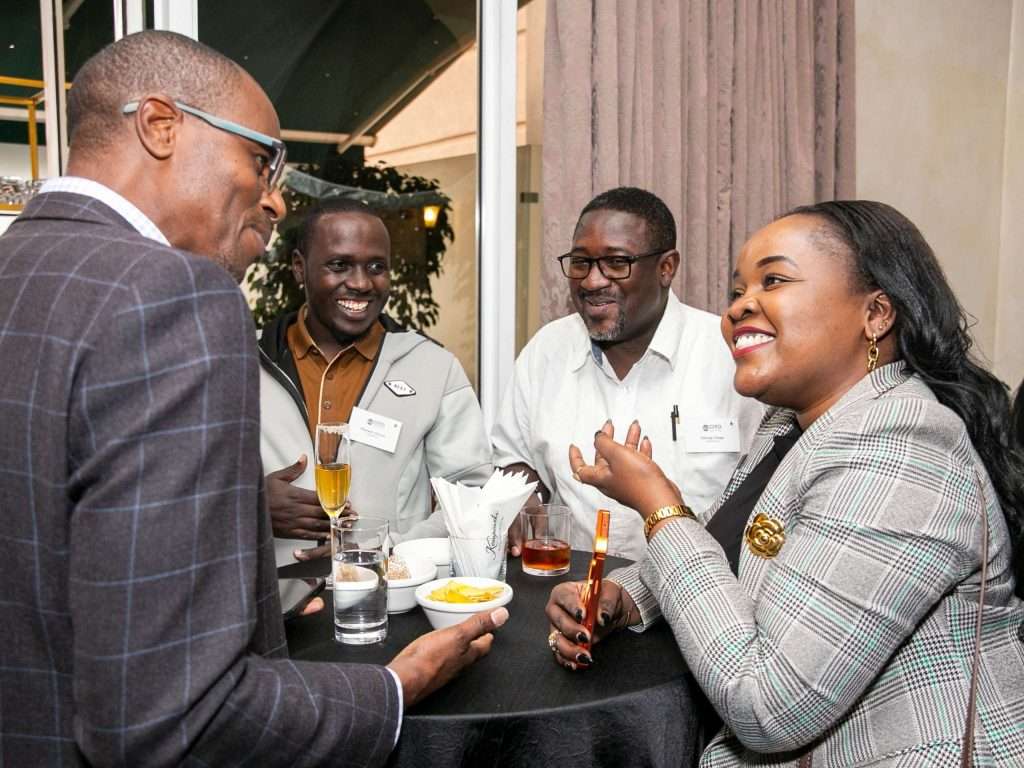
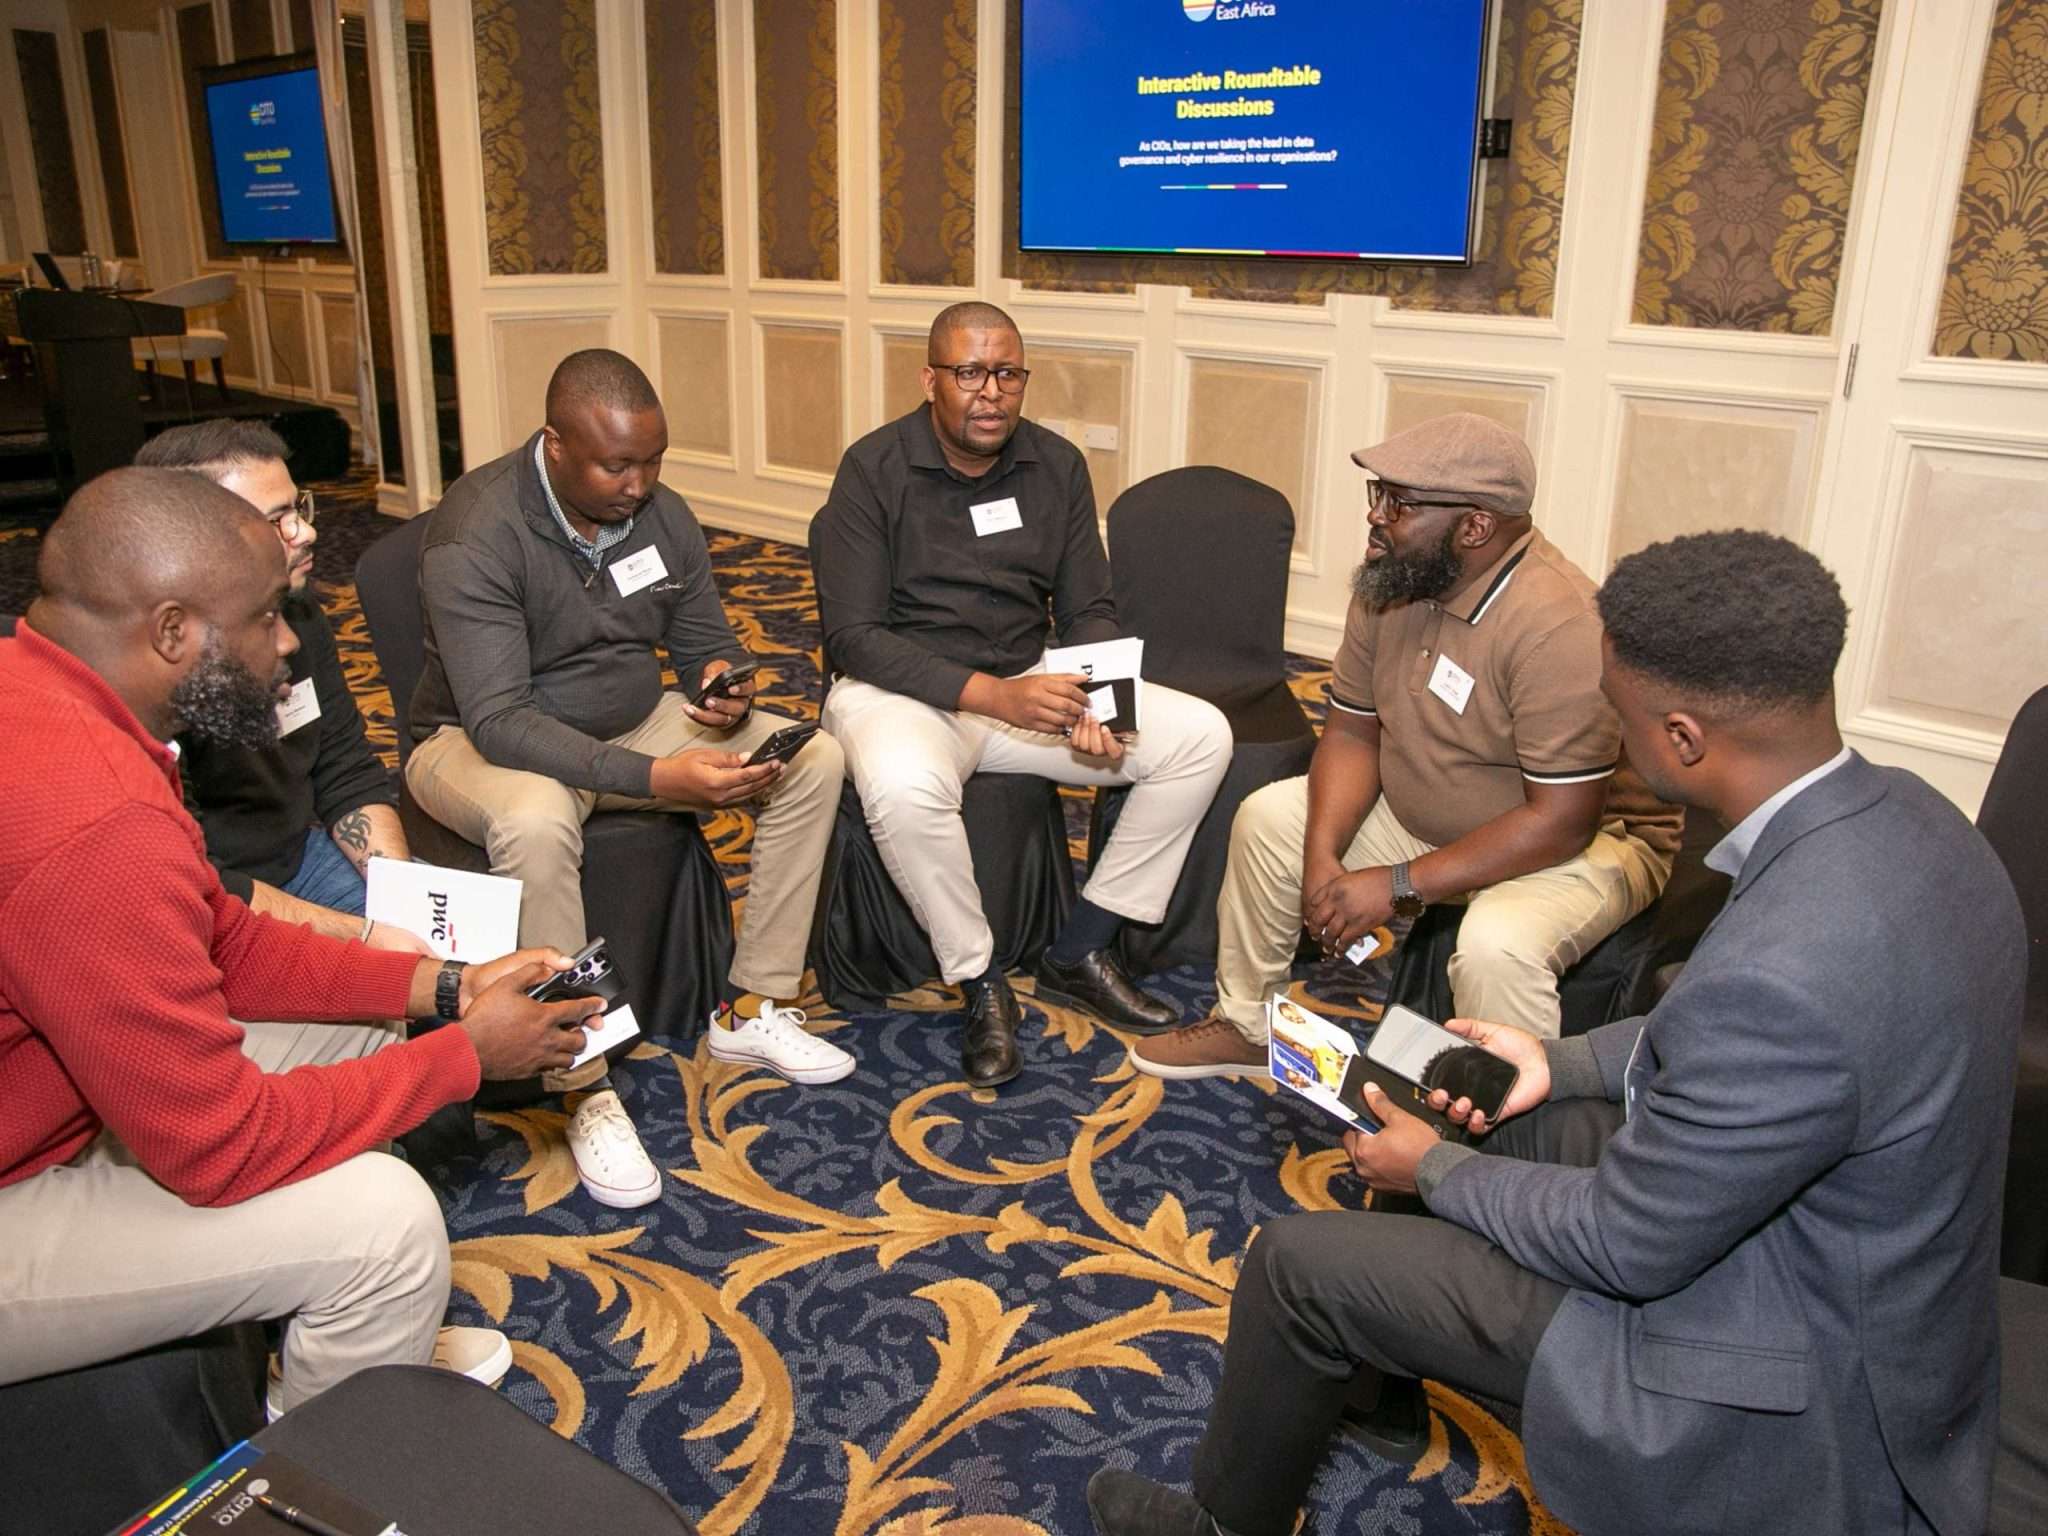
During the CITO East Africa Data and Cybersecurity Summit, attendees drawn from banking, healthcare, hospitality and the NGO sector broke into small groups to discuss how CIOs can take the lead in data governance and cyber resilience in organisations. The discussions proved an opportunity for CIOs present to share challenges they face and find solutions together.
The discussion in one group began with defining data governance beyond access and control.
"There is training, stakeholder management, cadence, and the underlying infrastructure," Rusell said.
Attendees also discussed the practical challenges of implementing governance, and regulatory challenges came up as a common thread across nearly every group.
"The policies we make are always competing with the different governance frameworks that come from the different regulators of these industries," an attendee said.
That tension showed up differently across sectors. In banking, one executive pointed to how inconsistently rules get applied from one institution to the next.
"We haven't seen a regulator who wouldn't want to see innovation in their industry. However, there's still an impediment in some way, shape, or form, especially around the banking sector, where they look at things on a case-by-case basis. So you might want to implement something, the regulator says no, but you can see clearly another bank is implementing the same," Juliet said.
Building frameworks that fit the business
Despite the friction, there was broad agreement that regulation isn't the enemy of good governance but a necessary part of it.
"If you don't have a framework, you will be on your own. These policies and strategies will help you at the end of the day. So set out frameworks that clearly state what you need to do around your data governance," Juliet said.
One recurring suggestion was that governance frameworks should be built around the specific objectives and risks of the business, particularly in sectors like healthcare where the stakes around data are higher.
"Healthcare is a very key component in terms of privacy of data, and our discussion was around how do you ensure that actually the right people access the right data during the actual work” Ibrahim said.
Getting boards to buy in
Even where frameworks already exist, attendees agreed that getting them adopted at the board level is often the harder task.
"It's hard to sell your data governance strategy to the board, most of whom are non-tech. Then the CFO is the next element, who has cost-saving targets approved by the same board," Rusell said.
A different group offered an alternative approach for board conversations, particularly for organisations working toward cyber resilience.
"The approach is not to promise them that we will not be attacked. It will happen. Instead, determine how likely it is that an event will happen, how fast you can realise that the event has happened, and how fast you can recover. If you can answer those three questions confidently, then your board should be confident,” Rusell said.
That same discussion pointed to monitoring and recovery as the practical backbone of resilience, rather than prevention alone.
"You should have monitoring, detection, and recovery of systems, so that you are able to react and recover quickly," Rusell said.
Shared accountability
The final theme to emerge from the roundtable was accountability, specifically the tendency for blame to fall unevenly when something goes wrong.
"Whenever you have a cyber attack, all eyes turn to the CIO, but when things are moving very well, all eyes turn to other executives. We need the board to also own some of these issues that come out of cyber attacks,” Juliet said.