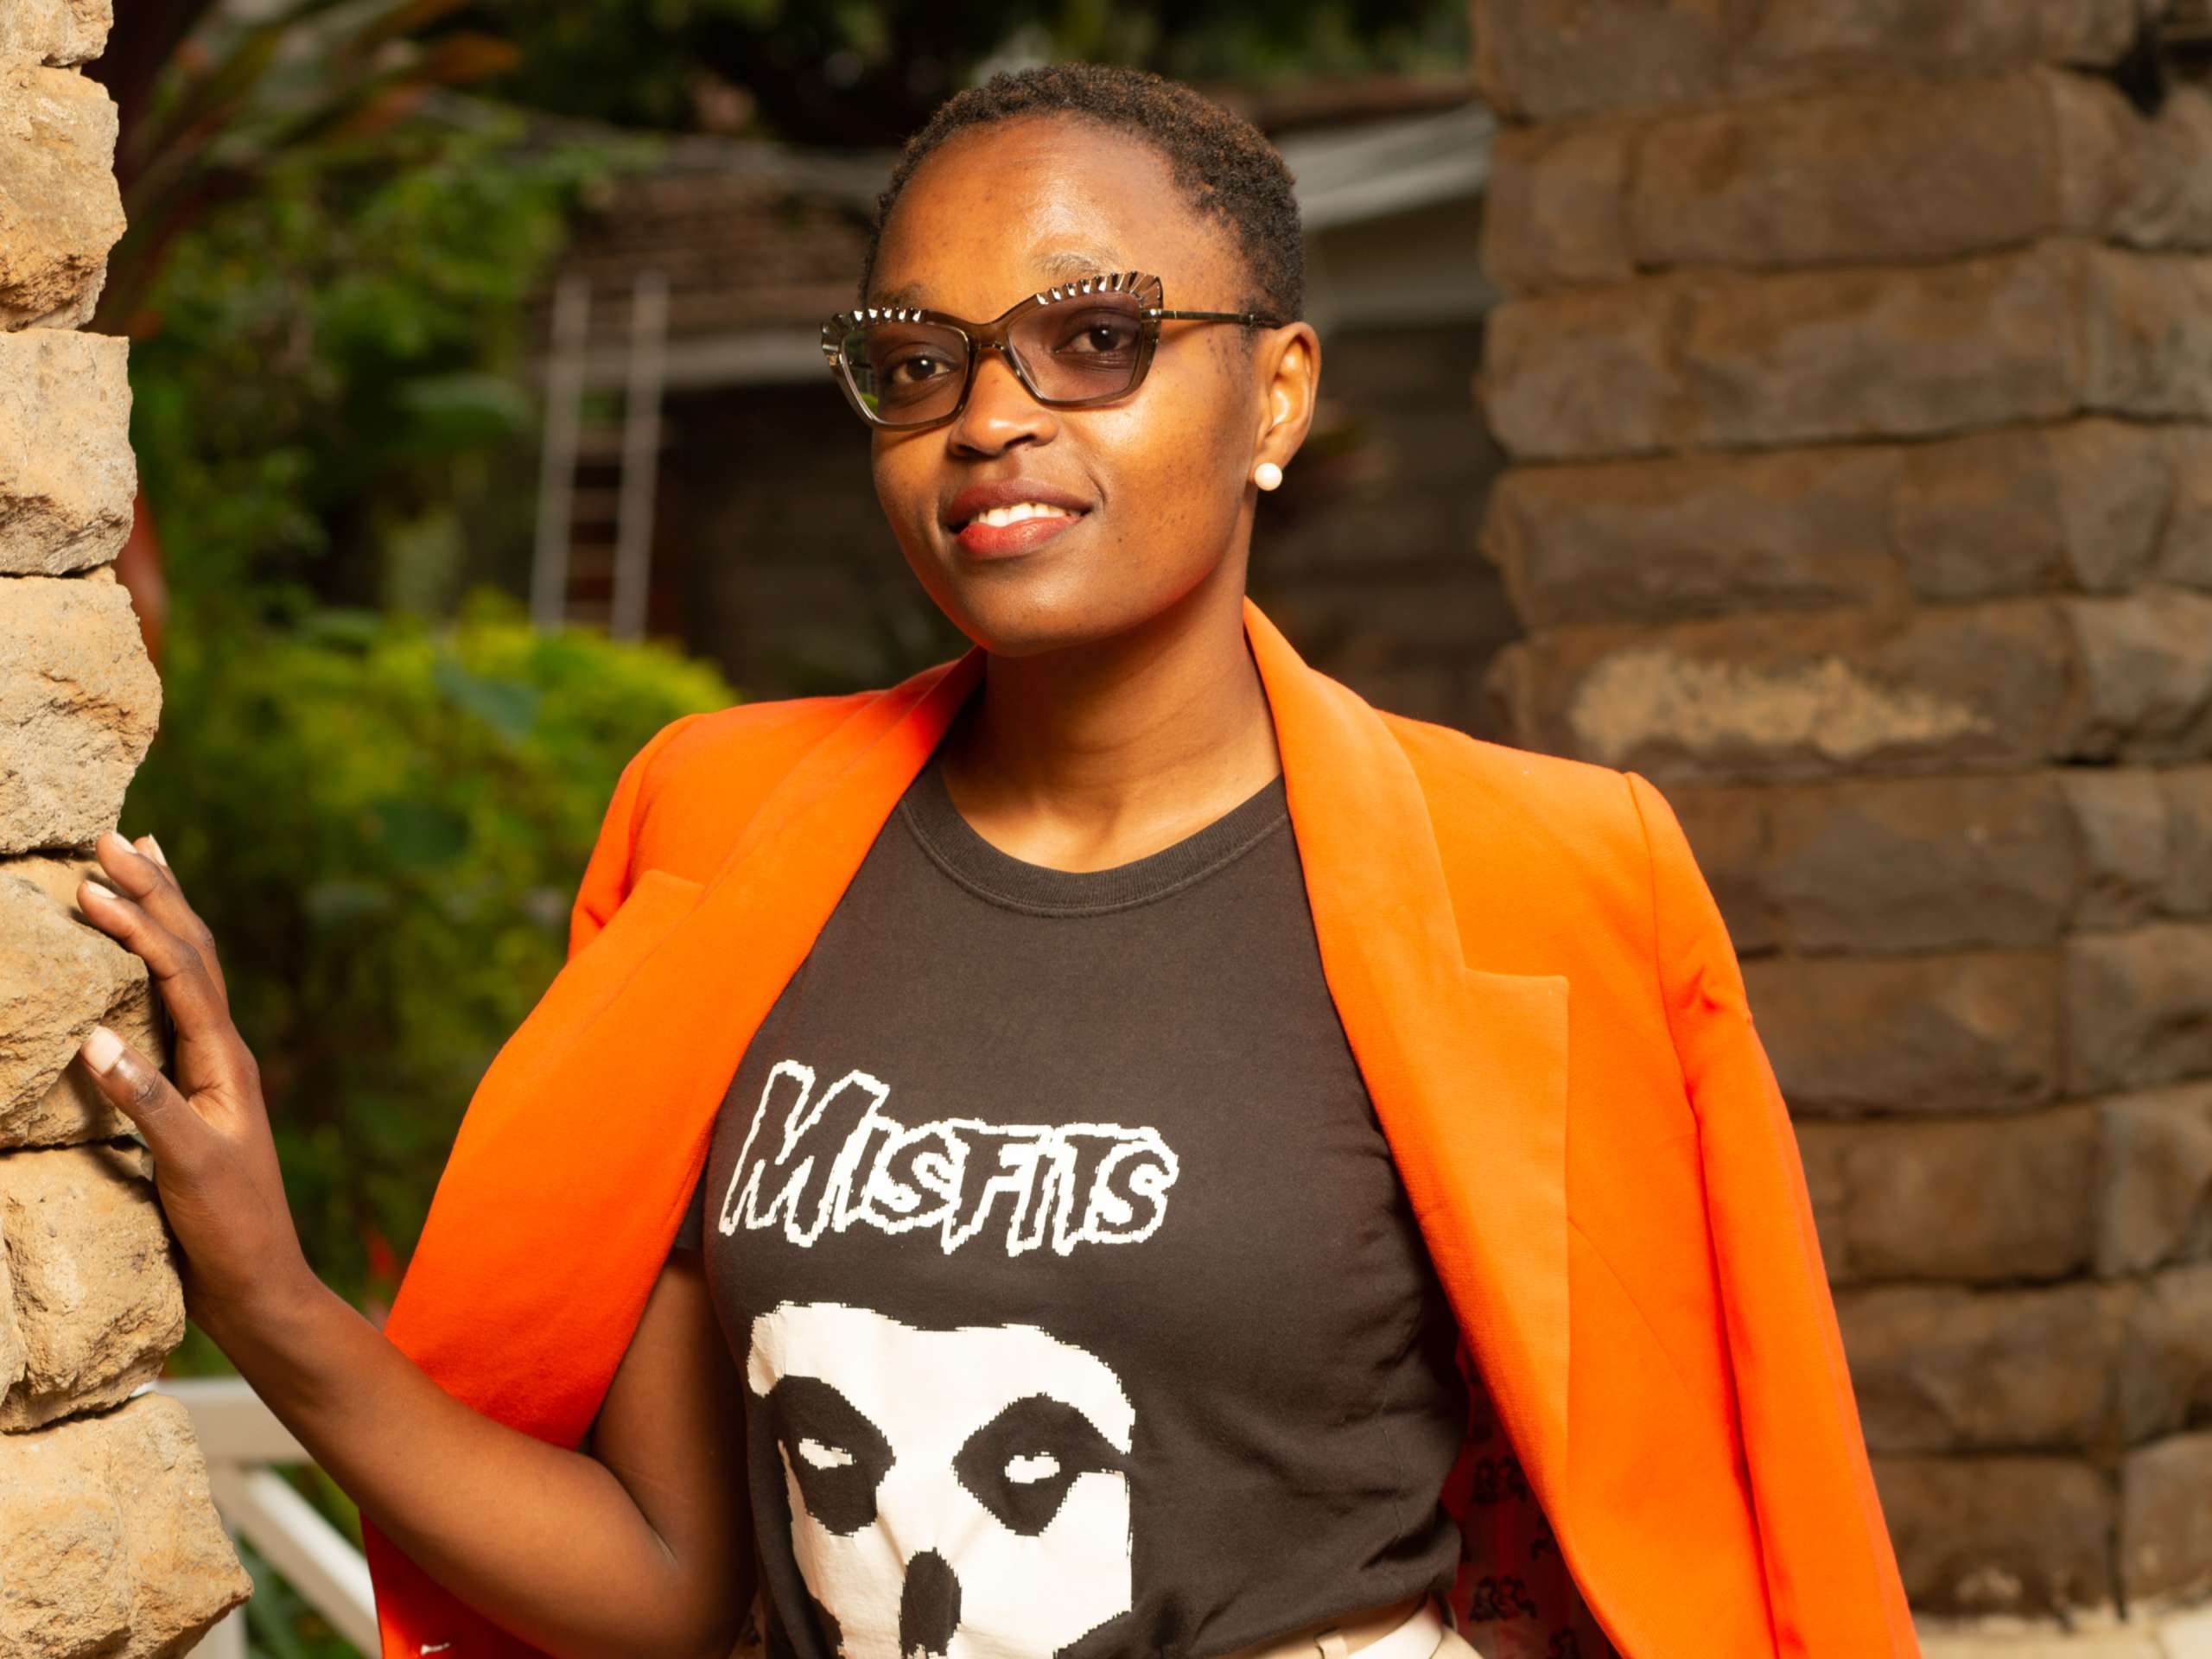
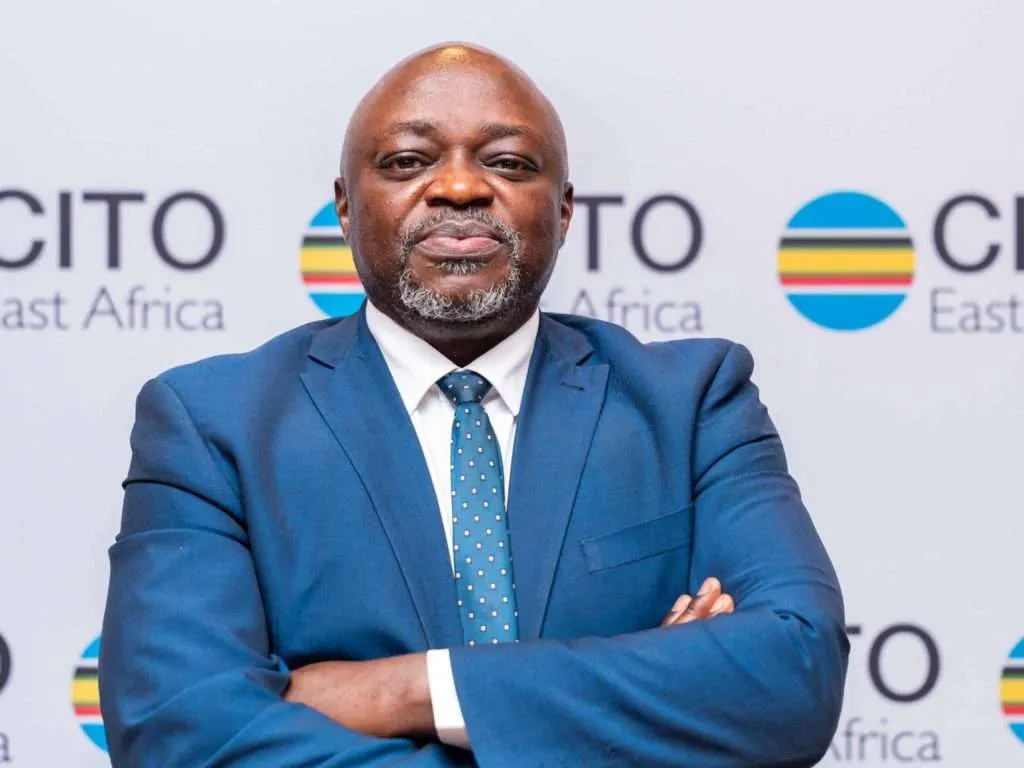
As digital payments become the way of life across East Africa, the nature of crime has evolved and become more sophisticated. However, for Ralph J C Ligallama, CIO at Equity knows this reality better than most. With over two decades of experience under his belt, he makes it clear that legacy safeguards are no longer effective in modern banking.
Ralph J.C Ligallama recalls a time before digital payments became an integral part of everyday life across East Africa. Back then, financial institutions relied heavily on perimeter security, firewalls, malware signatures, and predefined rules to protect their systems.
While these controls remain essential, Ralph believes that they are no longer sufficient on their own as financial institutions face an increasingly sophisticated threat landscape.
“Cybercriminals are moving beyond conventional attack methods and are now using automation and artificial intelligence to exploit vulnerabilities, compromise customer accounts, and execute fraudulent transactions at unprecedented speed. This means our defence mechanisms must evolve as well," he explains.
He advocates a shift towards intelligent, adaptive cybersecurity systems capable of understanding behaviour, identifying anomalies, and responding to threats in real time.
In digital payments, this transformation is particularly important.
“An AI-driven fraud prevention system, for example, can establish behavioural patterns based on how customers normally transact, including their transaction frequency, device usage, beneficiary relationships, transaction values, and interaction patterns,” he says.
Such a system can identify potential risks and trigger appropriate preventive measures before a transaction is completed any time unusual activity occurs.
"For example, if a customer normally takes three or four minutes to complete a transaction, and suddenly multiple transactions are initiated within seconds, that change in behaviour may indicate something unusual. AI can identify these deviations and assess the risk before the transactions are processed," he explains.
However, Ralph warns that transaction speed alone cannot determine whether fraud is occurring. Instead, effective AI fraud prevention requires multiple behavioural indicators, contextual intelligence, and appropriate customer verification.
While prevention might seem like the right course of action, Ralph explains that such threats are hard to detect, especially because most organisations do not have the right AI frameworks for such agents. Nevertheless, he also acknowledges that most organisations are now trying to build the required frameworks to detect and prevent threats.
He insists that vigilance, especially in financial institutions, is not optional because a security breach has the potential to bring operations to a standstill. For example, he recalls a 2024 incident, when a major regional bank in Kenya was hit by a severe ransomware campaign that forced its subsidiary operations completely offline for an entire month.
To survive, the institution had to revert to a style of banking from 30 years ago. Customers were forced to walk into physical branches with paper identification to withdraw cash manually. To make matters worse, because branch databases could not communicate with one another, a customer could only transact at their original home branch where physical records were kept.
“It was a very tough experience. Some guys contacted me for advice, and I told them there were two ways out: pay the ransom or go with your clean backup. Unfortunately, their backup was also attacked. The only option left was to restore data from two or three months back, accepting the total loss of all transactional data in between,” he recalls.
The crisis highlighted a dangerous flaw in how executive teams think about operational continuity. When systems suffer a total blackout, leadership faces existential pressure from regulators and the public alike. Ralph says the lesson from that incident was not merely technical, but systemic.
“A total shutdown means there is no bank. That is the point where you see chief executives collapsing under stress. When the attack takes down the core system, the bank effectively ceases to exist,” he says.
Re-engineering governance
Mitigating such severe risks is not solely a function of the IT department. Rather, Ralph opines that governance must change its identity within the enterprise, moving from a position of rigid restraint to one of active guidance. He further argues that governance should not be perceived as an obstacle to innovation but rather as a framework that enables organisations to innovate safely and responsibly.
"Governance should act as road markings instead of road blockers. It should guide us on where and how we can accelerate safely," he explained.
As banks increasingly bring software development in-house, internal environments have become remarkably dynamic. Young engineers and developer teams continuously test code and experiment within the network.
Although these capabilities improve innovation and responsiveness, they can also introduce new vulnerabilities when appropriate controls are not embedded into development processes.
“You might build a very big fence around your house with a heavy front door and expensive security appliances and still get compromised from the inside. Our Gen Z developers are doing experiments every day on the network. Intruders do not always break through the front gate anymore; they find an internal loop created during an experiment. That is why internal behavioural monitoring is just as critical as external perimeter defence,” he notes.
He also advocates for closer collaboration between technology, cybersecurity, risk, compliance, and business teams from the earliest stages of product development.
“Rather than introducing governance controls only when systems are ready for deployment, financial institutions should embed security and risk management throughout the innovation lifecycle. This approach enables institutions to maintain strong regulatory compliance while accelerating the delivery of new digital products and services,” he says.
The scholar in the C-suite
Ralph's perspective has been shaped not only by his over two decades of experience but also by his ongoing doctoral studies in artificial intelligence and technology management.
His research focuses on developing an AI-driven technology management framework to enhance fraud detection and prevention in real-time payment systems within East African financial institutions. The research also seeks to address the growing need for integrated approaches that combine artificial intelligence, technology governance, operational controls, human oversight, and regulatory requirements.
“The challenge is not simply to develop more sophisticated AI models but to establish the organisational capabilities necessary to deploy these technologies responsibly and effectively,” he explains.
This academic background influences not only his management style but also his daily personal habits. For example, he actively applies AI analytical models to evaluate personal investments and asset allocations.
Despite his advocacy for AI adoption, Ralph cautions against excessive reliance on automated systems. He notes that while AI can significantly improve productivity, accelerate analysis, support decision-making, and automate repetitive tasks, its output must still be subjected to professional judgment and appropriate verification.
“You have to remember that these tools can still give wrong information. They are meant to amplify human judgment, not replace it,he emphasises. Therefore, “AI should simplify your work and act as your personal assistant. Tasks that used to take two or three days can now be done in five minutes,” he says.
The future of cybersecurity in African banking
Ralph believes the future of banking technology leadership will depend on the ability to combine human expertise, intelligent automation, responsible governance, and continuous innovation. He especially emphasises that financial institutions must transition from predominantly reactive cybersecurity approaches to proactive, intelligence-driven prevention.
This requires investment in behavioural analytics, real-time threat detection, cyber resilience, secure technology architecture, and governance frameworks capable of adapting to emerging risks. Further, he insists that cybersecurity should no longer be viewed solely as a technology cost but as a strategic investment in customer trust, financial stability, and sustainable digital transformation.
“The future of cybersecurity is not simply about building stronger walls. It is about developing intelligent systems, resilient institutions, and governance structures that enable innovation while protecting customers and the financial ecosystem,” he says.