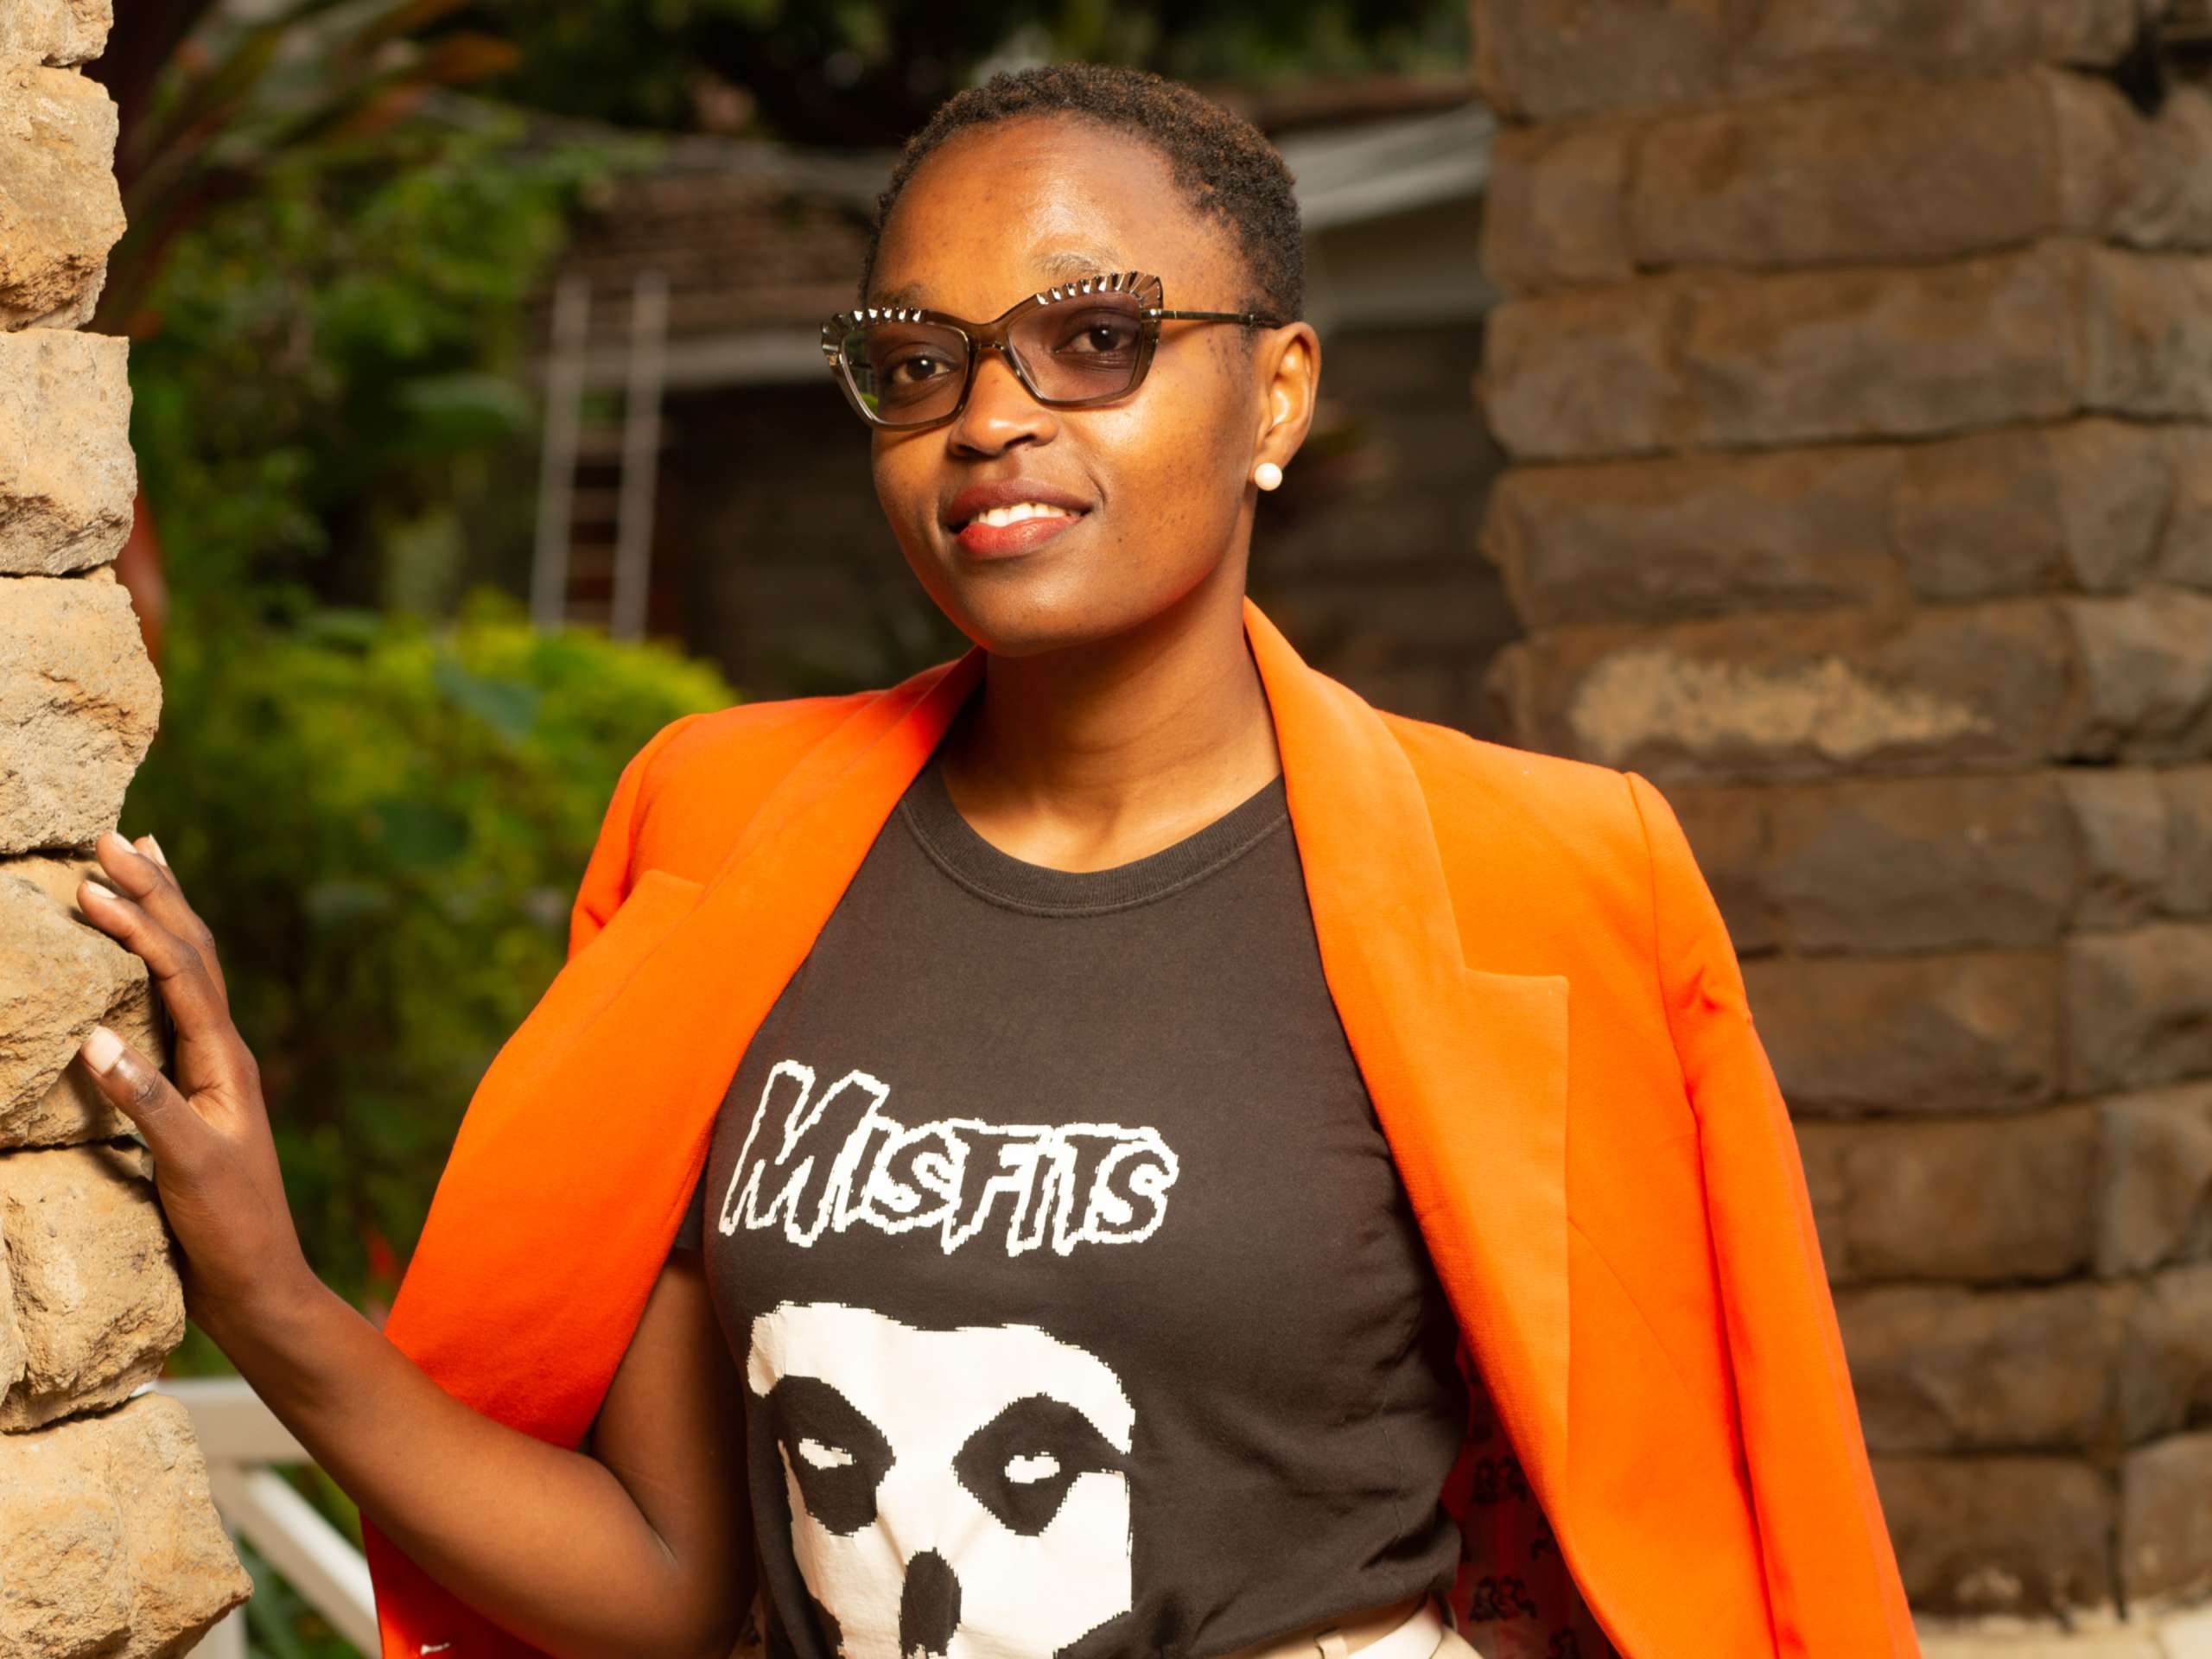

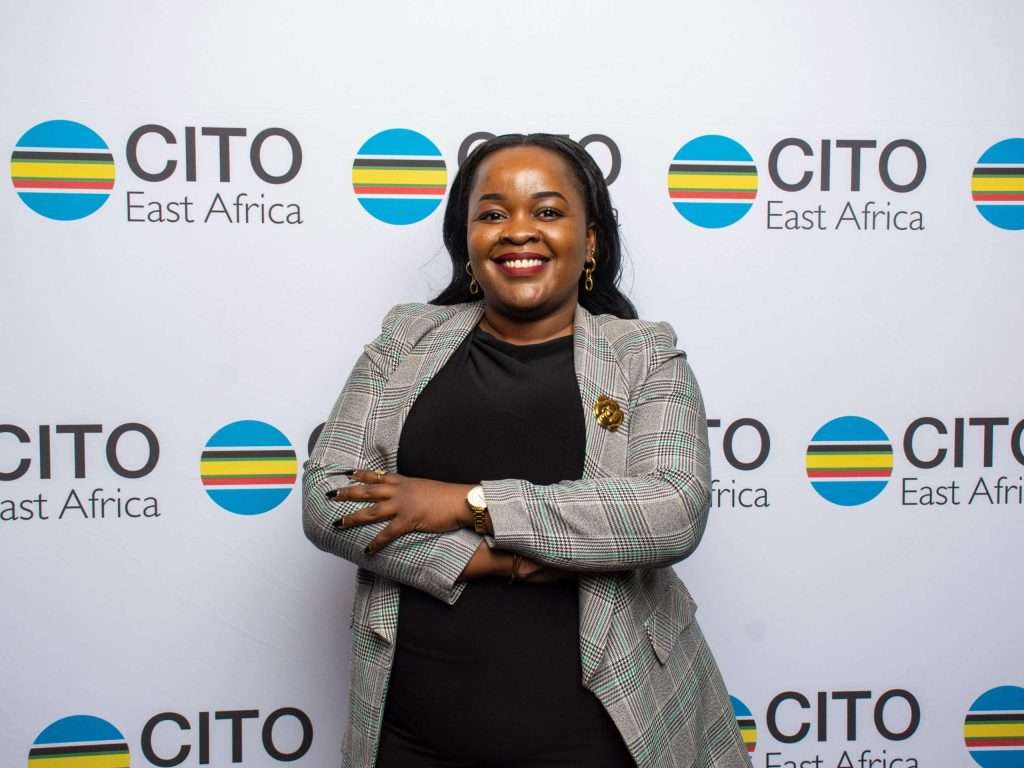
As head of technology services at Ecobank Uganda, Juliet Kyomugisha is at the forefront of the bank's digital transformation and cybersecurity efforts. She oversees technology projects, strengthens governance frameworks, and helps the bank stay ahead of evolving cyber threats. She shares how Ecobank leverages data, manages cybersecurity risks, and balances innovation with security.
There is so much data in the bank. How do you ensure that data is useful?
We have developed a number of dashboards that help business teams make informed decisions. For example, we monitor ATM usage to understand transaction volumes, values, and overall performance. This information helps finance teams assess the cost-benefit of certain systems and investments.
We also use data extensively for regulatory reporting, operational monitoring, and service management. Our monitoring tools provide insights that guide decisions on whether services should be upgraded, maintained, or discontinued. In addition, data from our IT service desk helps us identify the root causes of recurring issues and improve service delivery.
Who is responsible for the data in an organisation?
Data management is a shared responsibility. Before any regulatory information is submitted, the executive team must review and understand it. Ultimately, the managing director is accountable for ensuring that the organisation submits accurate information to regulators. At the same time, every department that generates, uses, or manages data is responsible for its accuracy and integrity. It is a collective effort across the organisation.
What are the biggest technology and cybersecurity risks that banks are facing today?
One of the biggest risks comes from third-party providers because organisations have limited visibility and control over what happens within their partners' environments. Banks must therefore put in place strong controls to protect themselves from potential threats that may originate from integrated partners and service providers.
Another major risk involves users. While people are often the first line of defense, they can also be a point of vulnerability. This is why we invest heavily in ongoing cybersecurity awareness training. We also promote accountability by conducting periodic simulations and spot checks, such as sending phishing-style links, to help staff recognise potential threats and strengthen their security awareness.
How has AI changed the risk landscape? Do you feel it is also contributing to some of these threats?
Yes, particularly from a data protection perspective. Many AI tools are publicly available, and organisations cannot always control what information users may upload or share with those platforms.
In my view, one of the biggest risks associated with AI is data leakage. Employees may unintentionally expose sensitive company information when using AI tools without understanding where that data is stored, processed, or shared. As organisations adopt AI, it becomes increasingly important to establish clear governance and usage guidelines.
How do you balance innovation while ensuring proper security?
The key is to start every innovation initiative with security in mind. Security should not be an afterthought.
For any new project, technology and security teams should be involved from the beginning because they are often able to identify risks that may not be immediately visible to business teams. When security considerations are addressed early, organisations can design appropriate controls and mitigations without slowing innovation. No system is completely risk-free, but identifying risks early makes it much easier to manage them effectively while still achieving business objectives.
What processes have you put in place for incident response?
While I have not personally experienced a major cybersecurity incident, it is important for every organisation to have a clearly defined incident response team and process in place.
When an incident occurs, the first priority is to quickly identify the source and contain the threat. Depending on the nature of the incident, this may involve isolating affected systems, temporarily shutting down services, or implementing other containment measures. If the issue relates to physical security, the relevant physical security teams must also be engaged. Effective incident response depends on having the right people, processes, and communication channels in place to respond quickly and minimize impact.